

AI agents can act. Can your organisation stop them?
- Recorded Live
71.8% of organisations surveyed allow AI agents to act on systems without human approval. Of those organisations, 75.5% cannot revoke the agents’ access.
Neil Gad
Chief Product and Technology Officer, RealVNC®
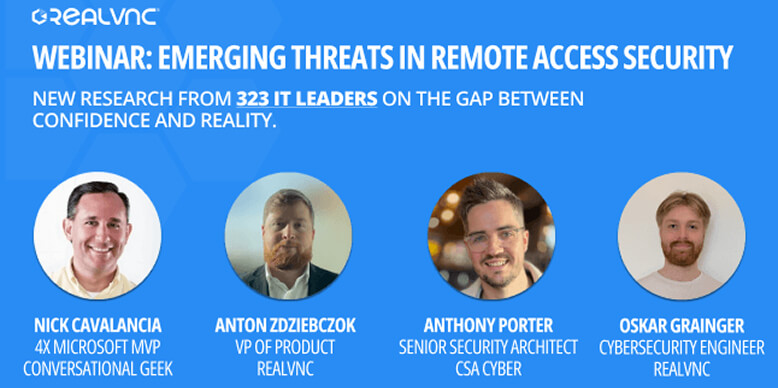
Nick Cavalancia
4X Microsoft MVP · Host
Anton Zdziebczok
VP of Product, RealVNC®
What you’ll learn
Who can hit the brakes? Why the organisations allowing autonomous action are often unable to revoke agent access.
Where agents can go. How agents are reaching legacy, OT and non-API systems, and what that means for access control.
What has already gone wrong. The incidents respondents reported, including operational disruption and data exposure.
What IT may not know about. The 39.2% reporting agent use without formal IT or security approval.
Which controls matter next. What respondents say they need, and the gap between confidence in oversight and the capabilities in place.
You’ll leave with a clearer set of questions to ask about agent access, approval, monitoring and revocation in your own environment.
Who should watch
IT, security and operational leaders responsible for AI agents, remote access, legacy systems or OT environments.
Watch the webinar on-demand
Fill in the form to watch the recording and get access to the full report.
A preview of the data
75.5%
Of organisations that allow agents to act without human approval cannot revoke agent access.
28%
Reported an incident involving an AI agent in the past 12 months.
42%
Of respondents who were very or extremely confident they would detect an agent acting outside its intended scope had no real-time monitoring in place.
Source: RealVNC 2026 Agentic AI Survey. Online survey of 227 IT and technical decision makers in the US, UK and Canada, fielded September 2026. The figures above have different respondent bases; the webinar will explain the findings in context.
The RealVNC 2026 Agentic AI Survey Report is now available
Our 2026 Agentic AI Survey asked 227 IT and technical decision-makers across the US, UK and Canada how far they let AI agents act, what those agents can reach, and what has already gone wrong.
The full report sets out the findings in detail, including:
- Why most organisations let agents act without approval, yet few can revoke that access
- How deeper agent access to legacy and operational systems makes agents harder to stop
- Why unsanctioned agent use is associated with more incidents
- Why confidence in detecting a rogue agent often outruns real-time monitoring
- Why the question is which controls matter, and where they sit
Watched the webinar? The report, together with the recording, is ready for you here.